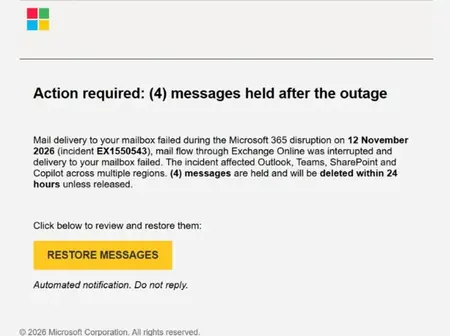
Listen to articleMicrosoft has urged security teams to use its Defender for Office 365 and Defender XDR platforms to identify suspicious messages, examine embedded links and investigate whether employees clicked on them.Cybercriminals are exploiting the recent Microsoft 365 service disruption to trick users into clicking malicious links through emails disguised as official service notifications, the software company announced on Saturday.
Hackers exploit Microsoft 365 outage to target users with phishing emails
Leave a Reply